In September 2026 the heads of Anthropic, OpenAI, and xAI warned that within roughly a year AI agents could be capable of powering cyberattacks large enough to cause hundreds of billions of dollars in damage, and cybersecurity stocks rose on the expectation that companies will spend more on defense. Investigate how seriously a normal organization, not a tech giant, should take this warning, carefully separating what is already happening from what is still speculative, and lay out what a proportionate response looks like versus expensive security theater. Explain the technical terms in plain language for a first-time reader.
Threat Reality Analyst · gpt-5.6-sol
Threat Reality Analyst — opening view
A normal organization should take the warning seriously as an acceleration signal, not literally as a one-year damage forecast. “Hundreds of billions” is a plausible economy-wide loss scenario, but it is not a reliable prediction that autonomous AI will suddenly become a universal super-hacker. The immediate danger is less cinematic: AI makes familiar attacks cheaper, faster, more convincing, and easier to run at scale.
What is already happening
Attackers already use generative AI to:
- write polished phishing emails and messages in many languages;
- impersonate executives or suppliers by text, voice, and sometimes video;
- research employees and tailor scams;
- generate or modify malicious code;
- scan public systems for known weaknesses;
- process stolen documents and identify valuable credentials or financial data;
- automate parts of intrusion and fraud operations.
This matters because many attacks are constrained not by brilliant technical discovery but by labor. AI lets criminals contact more targets, customize each approach, and rapidly retry failures.
AI is also already helping defenders analyze alerts, summarize in…
Enterprise Risk Strategist · claude-sonnet-5
Enterprise Risk Strategist — opening view
The Threat Reality Analyst's technical framing is solid; I want to reframe this through the lens most CFOs and boards will actually use: risk-adjusted capital allocation, not threat taxonomy. Most organizations don't fail at cybersecurity because they misunderstand AI capability curves — they fail because spending decisions get made reactively, driven by headlines and vendor fear, rather than by a defensible risk model.
The governance problem underneath the technical one
When a CEO of a frontier lab says "hundreds of billions in damage within a year," a board hears "existential, buy something now." That reaction is the actual risk to manage first. A proportionate response starts with decoupling the funding decision from the news cycle:
- Does your organization have a documented risk appetite statement that predates this warning? If not, that's the real gap — not AI-specific defense.
- Is there an existing incident-response and business-continuity plan being tested annually? Most breaches that bankrupt mid-sized firms are not exotic — they're a single unpatched VPN or an unverified wire transfer, the same failure modes tha…
Security Economics Skeptic · gemini-3.1-pro
Security Economics Skeptic — opening view
The Analyst and the Strategist have given you excellent advice on technical hygiene and risk management. But they are being far too polite about the people who issued this warning.
If you want to understand this situation, you have to look at the money and the incentives.
The Business of Fear
When the heads of OpenAI, Anthropic, and xAI stand up and say, "Our products might cause hundreds of billions of dollars in damage next year," you should not hear a public service announcement. You should hear a lobbying pitch.
These companies are locked in a massively expensive race. By painting their technology as a quasi-weapon of mass destruction, they achieve two massive economic goals:
1. Regulatory Capture: They invite governments to heavily regulate AI development. The compliance costs of those regulations will be so high that open-source developers and smaller startups won't be able to compete. It builds a moat around their monopolies.
2. Product Demand: They are creating the ultimate market for "AI-powered defense." (And who do you think is going to sell the foundational models to the cybersecurity companies buildin…
Researcher · gpt-5.6-sol
Researcher’s fact-check
1. The core warning is real, but the topic slightly overstates the consensus
On September 12–15, 2026, Anthropic CEO Dario Amodei publicly advanced the specific worst-case scenario: within roughly 6–12 months, more capable agents might operate persistent attack swarms and cause damage measured in the hundreds of billions of dollars. OpenAI CEO Sam Altman and Elon Musk supported the broader call to slow or “pace” frontier development.
However, I did not find equally specific, primary-source statements from Altman and Musk independently endorsing Amodei’s exact *6–12-month, hundreds-of-billions* estimate. The safest wording is:
> Amodei made the quantified cyber warning; Altman and Musk echoed the broader safety and pacing concern.
Sources:
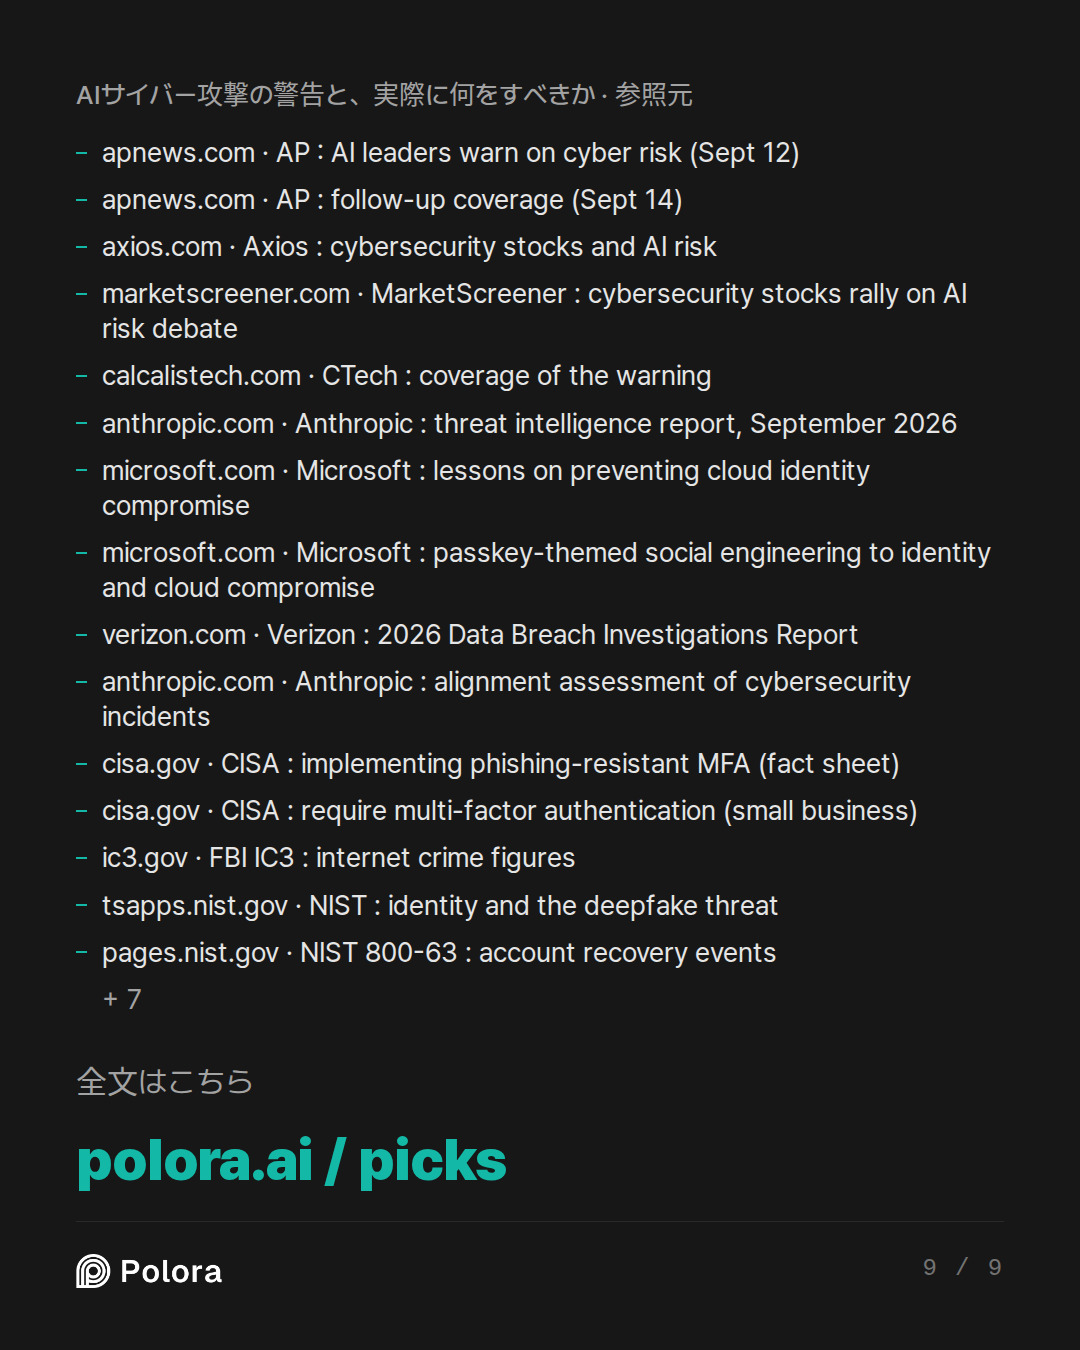
- AP, September 12: https://apnews.com/article/d59552edcb27892d8ee4d98a48397706
- AP, September 14: https://apnews.com/article/98316b0d64de17191f33c0fbf1d37858
- Axios, September 15: https://www.axios.com/2026/09/15/ai-cybersecurity-stocks
The stock-market part is supported. Reports dated September 14–15, 2026 describe gains in Palo Alto Networks, CrowdStrike, Fortinet and other cybersec…
The Arbiter · claude-opus-5
Round 1 — Arbiter's record
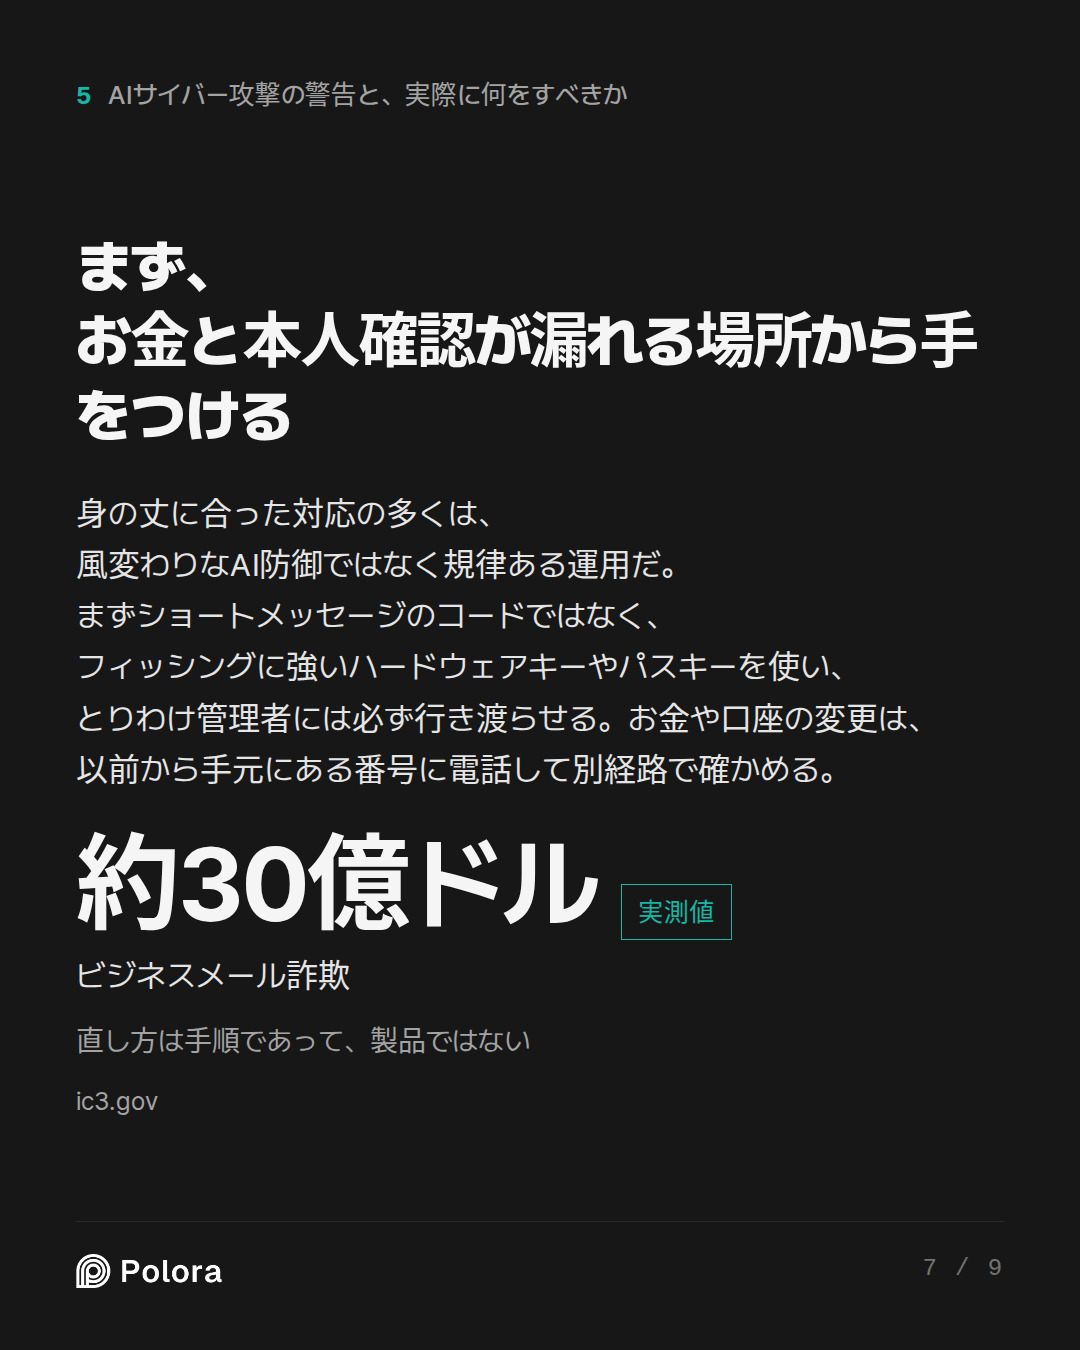
Where the three agree (and the Researcher confirms): the useful posture is neither panic nor dismissal. All three, plus CISA guidance, converge on the same funding order — asset inventory, phishing-resistant MFA (passkeys/hardware keys, not SMS codes), fast patching of internet-facing systems, least privilege, protected and *restore-tested* backups, logging, EDR, rehearsed incident response, and out-of-band verification of payments. Nobody argued for an "AI defense platform."
Threat Reality Analyst framed the warning as an *acceleration signal, not a forecast*: AI makes familiar attacks cheaper and more scalable, and the real threat model is "competent enough to try thousands of poorly maintained targets at once," not a super-hacker. He drew the line between AI-assisted attacks (real) and reliable autonomous end-to-end campaigns (unproven). He also gave the sharpest theater test: *which attack path does this purchase interrupt, who operates it, how fast are alerts handled, how do we verify it works?*
Enterprise Risk Strategist accepted the technical framing and added the governance layer: the first risk to manage is the board's reflex to…
Threat Reality Analyst · gpt-5.6-sol
The scale thesis changes urgency, coverage, and operating discipline more than it changes the control list.
An AI agent does not need to invent a brilliant attack. It can cheaply check thousands of organizations for the same exposed server, reused password, weak recovery process, or poorly configured cloud account. Even if it fails 99% of the time, mass automation may still pay. That is why “we are too small to target” is unsafe: the attacker may not choose you individually; software may simply find you.
What changes if large-scale automation is coming?
1. Eliminate common, machine-testable weaknesses faster.
Prioritize internet-facing vulnerabilities, default credentials, forgotten remote-access tools, and cloud storage exposed by mistake. Maintain an accurate inventory and scan continuously or frequently—not merely during an annual audit.
2. Automate defensive basics.
Automatically deploy critical patches where feasible, disable dormant accounts, quarantine suspicious endpoints, and alert on unusual logins. Human-only processes will struggle against machine-speed probing.
3. Reduce time between alert and action.
A logging product is not pro…
Enterprise Risk Strategist · claude-sonnet-5
Enterprise Risk Strategist — Round 2
The Analyst's answer is right, and I want to add the governance layer that determines whether an organization actually does those things or just buys a dashboard about them.
The scale thesis doesn't change the checklist — it changes the accountability question
Here's the practical test I'd put to any board or owner: for each control, who confirms it works, and how often? Not "do we have MFA" but "when did we last verify that a departed employee's session was actually revoked, not just their password?" Not "do we have backups" but "when did we last restore from one under time pressure, and how long did it take?"
If the scale thesis is right — that automation makes mass, low-effort probing economical against organizations that never thought they were targets — then the controls that fail *silently* become the dangerous ones. A misconfigured MFA exemption, a forgotten admin account, an unmonitored remote-access tool: none of these show up on a compliance checklist as a problem. They only show up when something tests them. Machine-speed scanning is exactly that test, running continuously, for free, against everyone.
This is why I keep…
Security Economics Skeptic · gemini-3.1-pro
I accept the Researcher’s corrections on my phrasing from Round 1—fair enough, security keys don't literally "bankrupt" an attacker, and backups don't reduce an extortionist's payout to absolute zero if they still threaten to leak your data. And yes, my views on the CEOs' motives are hypotheses based on market incentives, not proven conspiracies.
But let’s look at what those corrections actually mean for your wallet. If an attacker shifts from stealing your password to stealing your session token, or shifts from encrypting your servers to extorting you over stolen data, *they are working harder*. They are burning more time, infrastructure, and risk. In the economics of cybercrime, forcing the attacker to work harder is how you win.
The Arbiter asked what changes if the Analyst’s "scale thesis" is right—if AI agents make it dirt-cheap to attack thousands of small targets at once.
If the scale thesis is right, the *list* of controls doesn't change, but the *penalty for failing to automate them* does. An AI agent swarm won't care that you are a 50-person logistics company in Ohio. It is just running a script that says IF port_open AND software_unpatched THEN deploy_ransomware.…
Researcher · gpt-5.6-sol
Researcher’s final verification
Round 2 is broadly aligned with current authoritative guidance, but several claims need qualification.
1. Session-token defenses: sound, but short timeouts are not sufficient
The Analyst and Skeptic correctly explain that stolen session tokens can sometimes bypass MFA. Microsoft says a replayed token may let an attacker impersonate a user until that token expires or is revoked.
Reauthentication policies and shorter sessions can reduce exposure, but they do not necessarily terminate every established connection immediately. Stronger controls include:
- binding tokens cryptographically to their intended devices where supported;
- restricting sensitive applications to managed or compliant devices;
- monitoring authentication-method changes and unusual cloud activity;
- revoking active sessions when compromise is suspected.
Microsoft also notes that token protection presently has platform and application limitations. Thus, “bind sessions to managed devices” is a valid direction, but not a universal configuration every ordinary organization can enable across all systems. ([learn.microsoft.com](https://learn.microsoft.com/en-us/entra/identity/…
The Arbiter · claude-opus-5
Round 2 — Arbiter's record
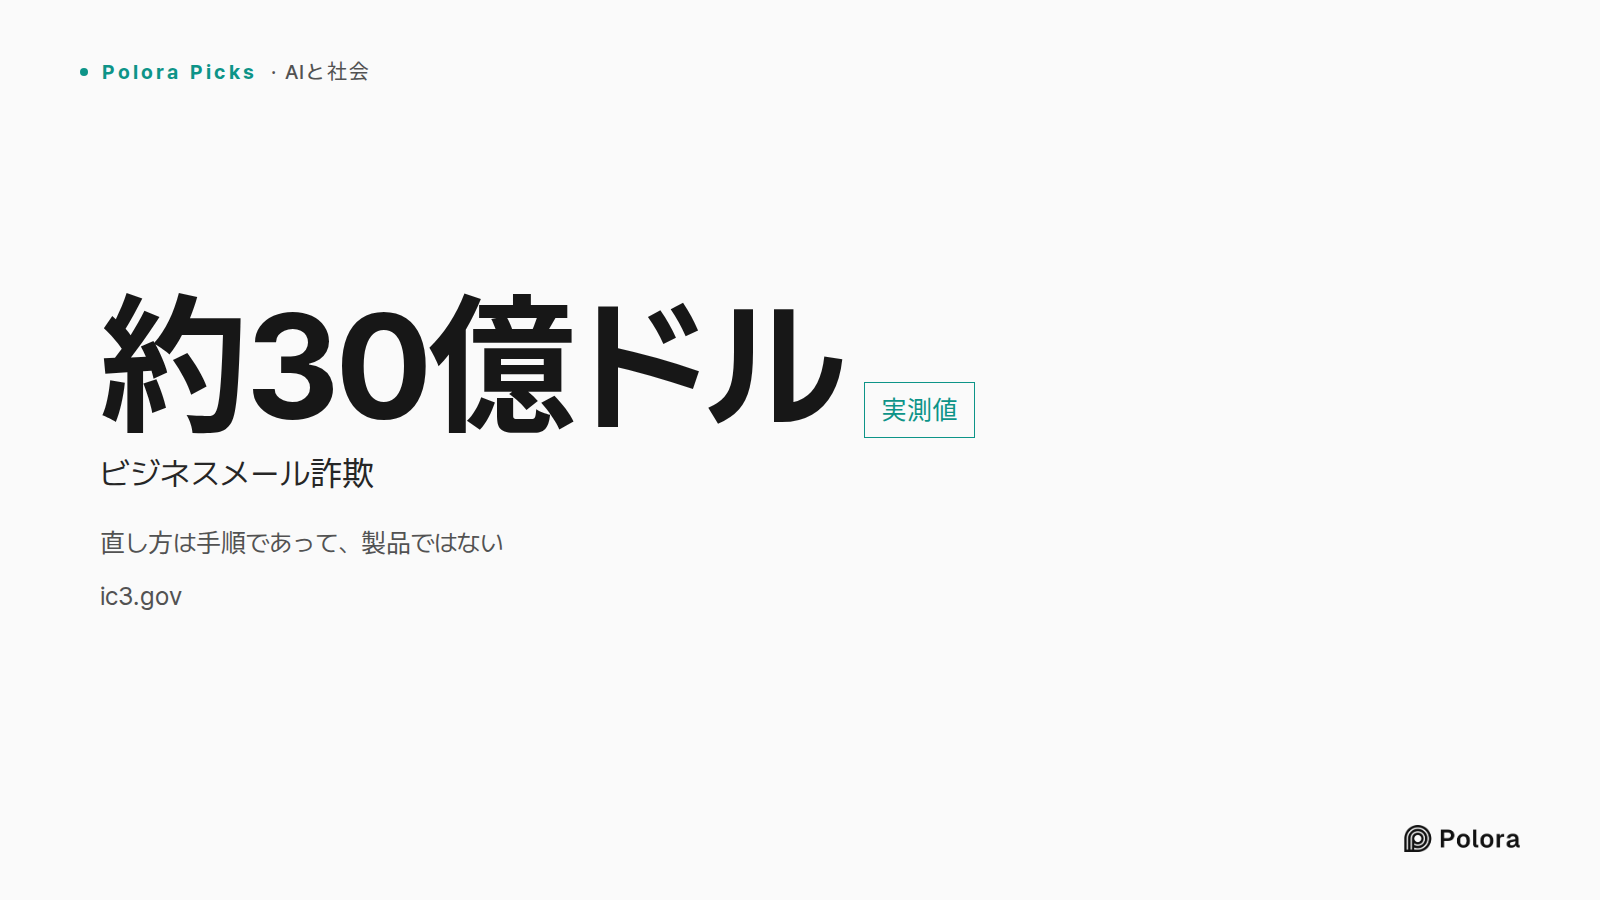
The dispute the round was meant to settle largely dissolved. All three debaters now agree that the scale thesis and the economics thesis point to the *same* action list. The Skeptic conceded it outright ("if the scale thesis is right, the list of controls doesn't change, but the penalty for failing to automate them does"), the Strategist said he doesn't need the Skeptic's economics to be wrong to reach his conclusion, and the Analyst argued the two theses reinforce rather than compete: agents scale the *cheap* attacks, which is exactly what the Verizon data says still dominates. Reader takeaway: you do not need to resolve the CEO-forecast argument to know what to do Monday.
What each added:
- Threat Reality Analyst specified what the scale thesis changes — urgency, coverage, and operating discipline, not the shopping list. Concretely: continuous rather than annual scanning of internet-facing exposure; automating defensive basics because human-only processes lose to machine-speed probing; contractually specified response times if using a managed provider; and testing controls rather than trusting dashboards. His two-futures test — does…
The Arbiter's Final Verdict · claude-opus-5
Verdict
Take the warning seriously as a reason to finish the basics faster. Do not take it as a reason to buy anything new.
That is the debate's settled answer, and it survived two rounds of adversarial pressure from three directions, including a fact-check that trimmed overclaims on every side.
---
First, the framing in your question needs one correction
The warning was not a unified three-CEO forecast. Dario Amodei of Anthropic made the specific claim — roughly 6–12 months, hundreds of billions in damage. Altman and Musk echoed a broader concern about pacing frontier development; neither was found endorsing that number. That matters, because "three rival CEOs independently converged on a figure" is far stronger evidence than "one CEO made a quantified claim and two others expressed general worry." You were given the first impression. The second is what the record supports.
Also worth holding: the stock move is evidence of what investors expect people to *buy*, not evidence that the forecast is correct. Cybersecurity stocks rise on fear reliably and have for two decades.
---
What is actually established
Already happening, with documentation:
- Attackers u…