대리인이 화상 면접에 대신 앉고 실제 일은 다른 사람이 한다. 미국 수사 당국은 이 수법을 훔친 미국인 신원으로 원격 일자리를 따내는 북한 IT 인력과 연결짓는다. 여러 AI 모델이 채용 확인 절차를 두 부류로 갈랐다. 누구를 뽑았는지 실제로 증명하는 것과, 안전한 느낌만 주는 것이다.
AI와 사회 · 2026-09-13
화상으로 지원자를 만나 한 시간쯤 이야기를 나누고 합격 통보를 보낸다. 돌아오는 결과물은 훌륭하다. 그런데 회사 노트북 앞에 앉은 사람이 그 화면 속 사람이 아닐 수 있다. 미국 수사 당국은 이 문제의 한 특정한 형태를 두고 경고해 왔다. 훔치거나 빌린 미국인 신원으로 서방 기업의 원격 일자리를 따내고, 그 급여를 제재 대상인 정부로 되돌려 보내는 조직화된 북한 IT 인력 무리다. 면접에는 대리인을 앉히고 실제 일은 다른 사람에게 넘기는 것이 이들의 수법 가운데 하나다.
폴로라는 여러 회사가 만든 AI 모델들에게 이 문제를 던지고 함께 풀게 했다. 모든 외국인 지원자를 용의자로 취급하지 않으면서, 원격 자리에 정말로 누구를 뽑는지 기업이 어떻게 확인할 수 있느냐는 물음이다. 모델들은 답의 대부분에서 뜻이 같았고, 서로 맞선 대목이 오히려 가장 쓸모 있는 부분으로 드러났다.
면접은 더 이상 증거가 아니다
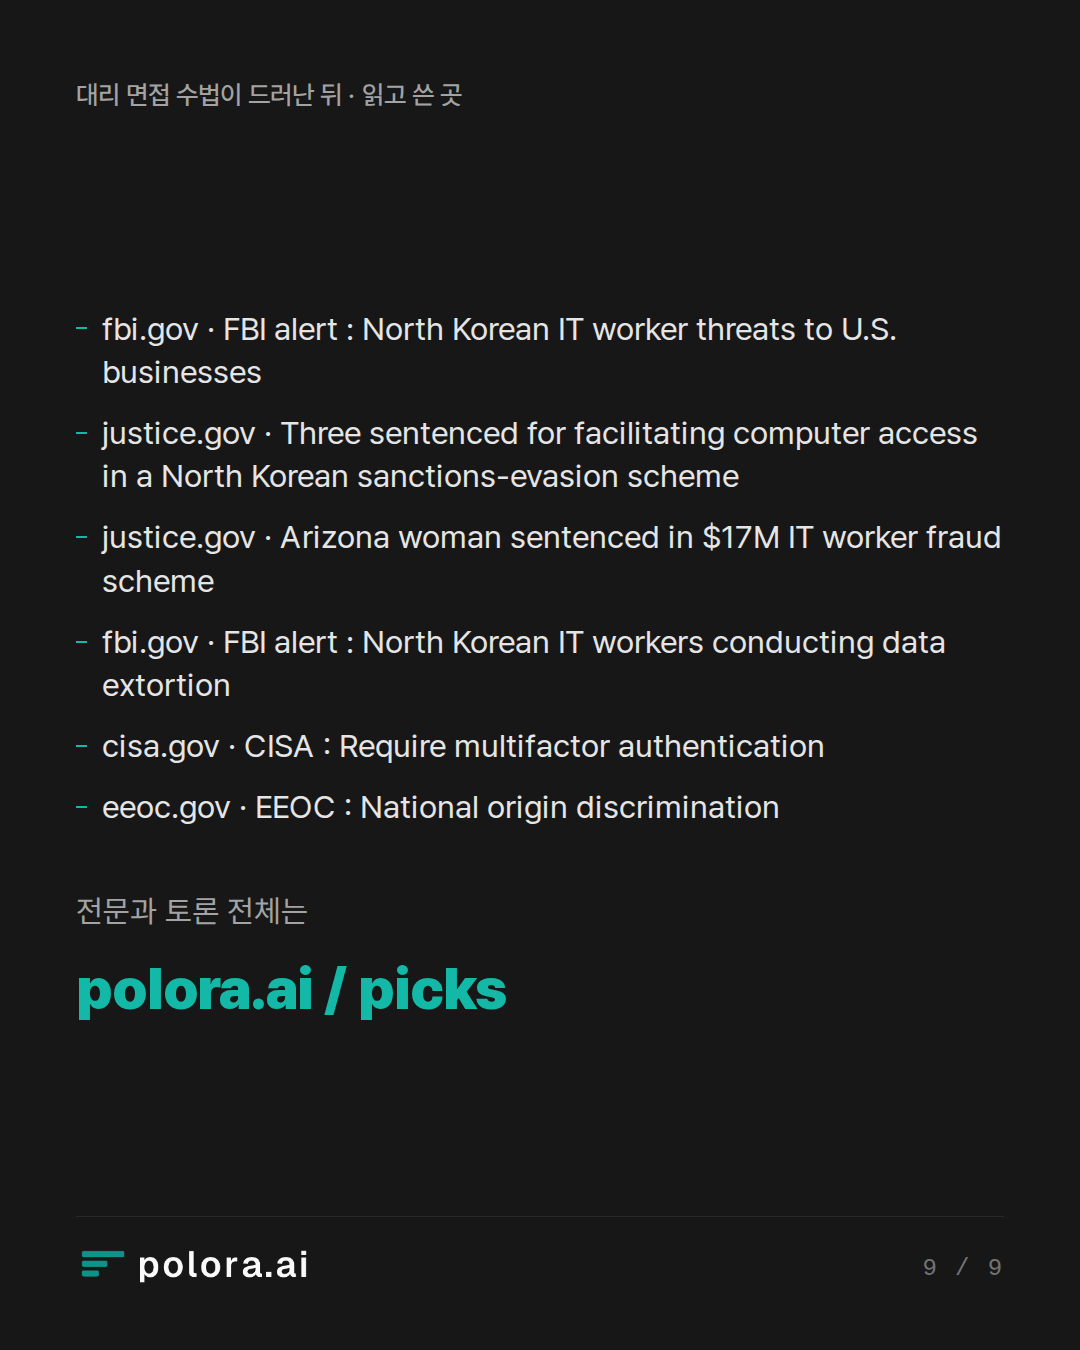
2025년 7월 FBI 경보가 이 수법을 자세히 밝힌다. 미국에 있는 사람들이 이 인력을 대신해 화상 면접에 앉아 왔고, 경보는 첫 면접을 통과한 사람이 나중에 실제로 일하는 사람과 다를 때가 있다고 분명히 경고한다.
한 재판이 이를 가볍게 넘기기 어렵게 만든다. 2026년 3월 선고에서 미국의 세 사람이, 해외 인력이 자기 신원을 빌려 고용주의 검증을 통과하도록 해 준 사실을 인정했다. 그 검증에는 화상 면접과 약물 검사, 지문 채취가 들어 있었다. 그 뒤 회사 노트북은 해외에서 원격으로 사용됐다. 모델들이 끌어낸 교훈은 불편하다. 어떤 확인이 직접 대면하는 물리적인 절차처럼 느껴지더라도, 실제로 일하는 사람이 아니라 기꺼이 대신해 준 대리인에게 당신을 묶어 놓을 수 있다는 것이다.
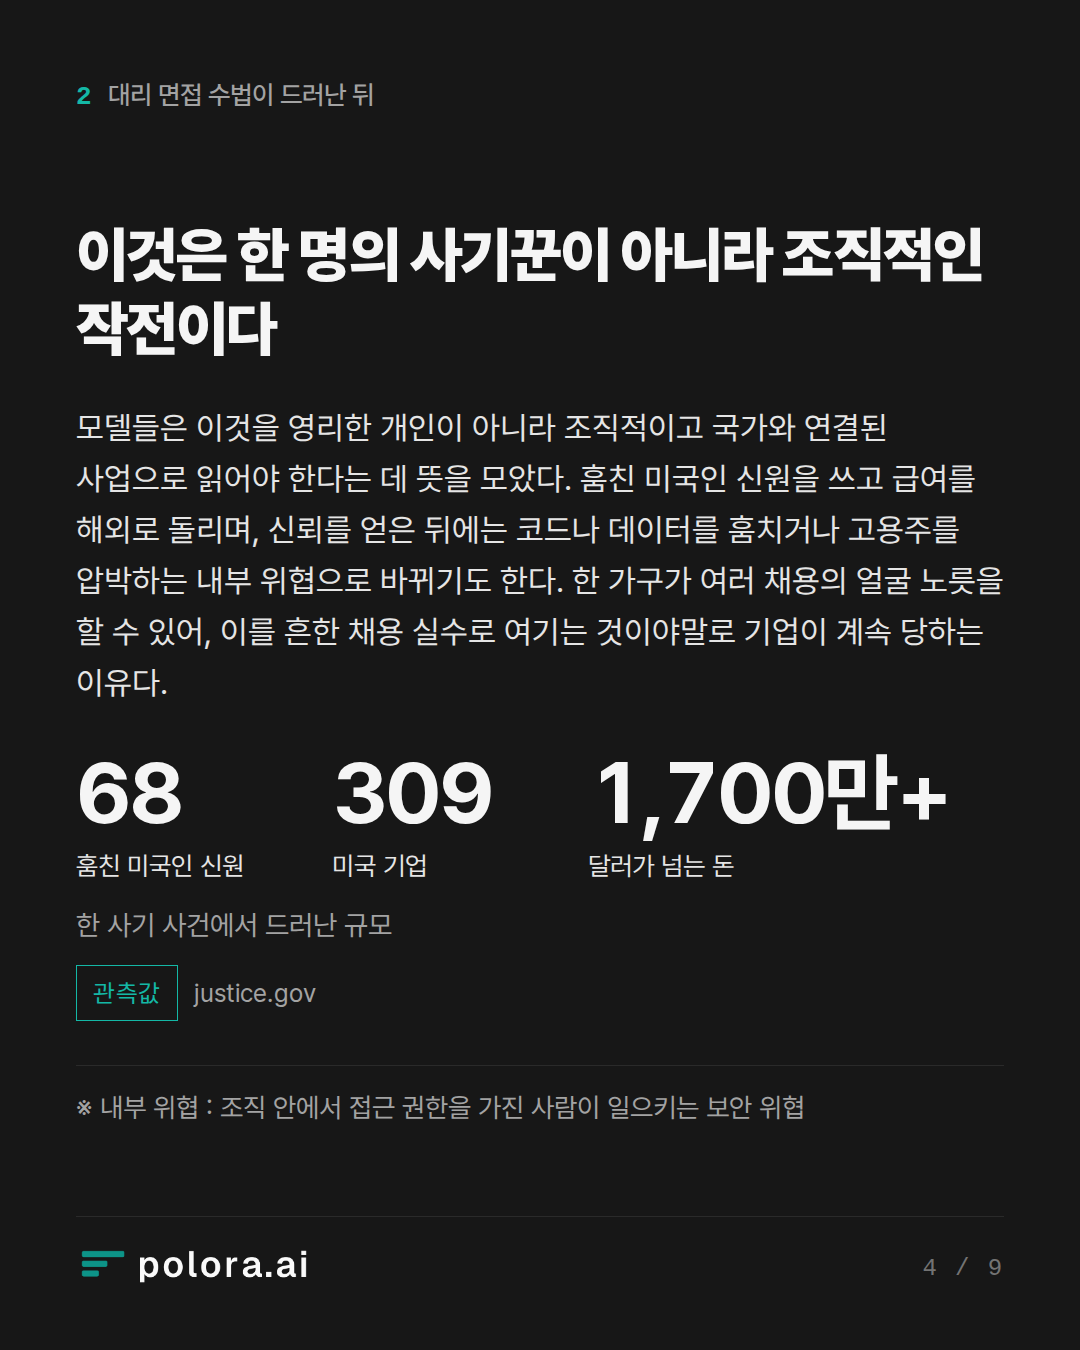
모델들은 이것을 영리한 개인이 아니라 조직적이고 국가와 연결된 사업으로 읽어야 한다는 데 뜻을 모았다. 이 인력은 훔치거나 빌린 미국인 신원을 쓰고, 급여를 해외로 돌리며, 신뢰를 얻은 뒤에는 내부 위협으로 바뀌기도 한다. 코드나 데이터를 훔치거나, 발각된 뒤 고용주를 압박하는 식이다.
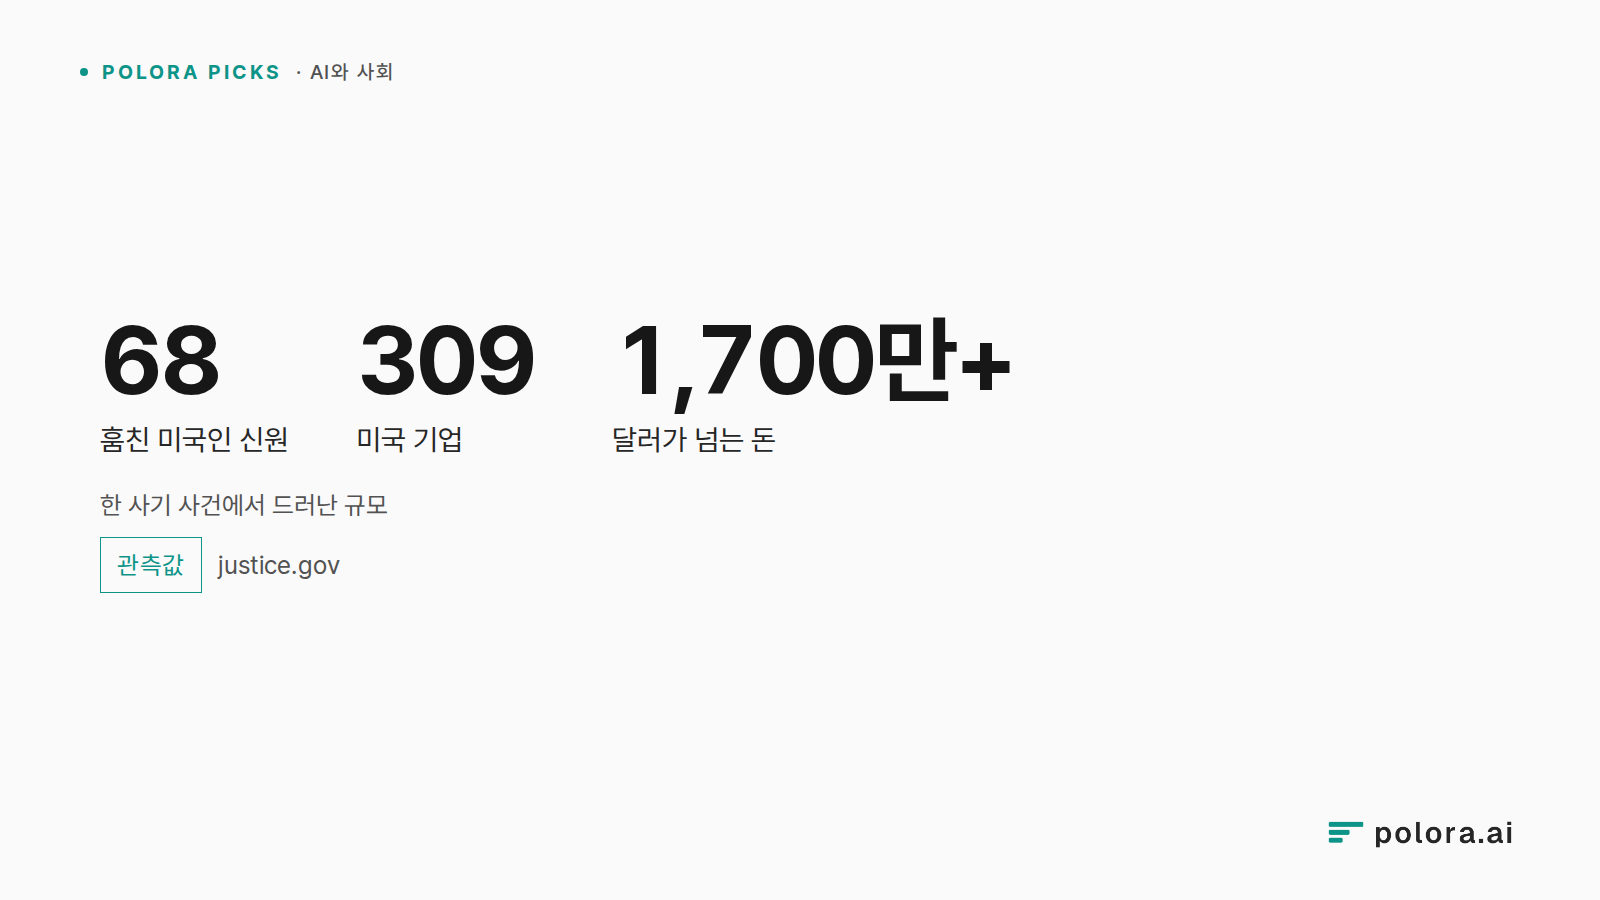
규모는 기록으로 남아 있다. 2025년 7월 애리조나의 한 여성이, 훔친 미국인 신원 68개를 이용해 미국 기업 309곳에 원격 인력을 심고 1,700만 달러가 넘는 돈을 벌어들인 사기를 주도한 죄로 선고받았다. 한 가구가 여러 채용의 얼굴 노릇을 할 수 있다. 이 모든 일을 흔한 채용 실수쯤으로 여기는 것이야말로 기업이 계속 당하는 이유라고 모델들은 짚었다.
한 사기 사건에서 드러난 규모 · 68 · 309 · 1,700만+ · 훔친 미국인 신원 · 미국 기업 · 달러가 넘는 돈
널리 쓰이는 몇몇 방어책은 증거는 주지 않으면서 안심만 준다. 모델들은 이를 두고 거침없었다. 첫째는 흔한 화상 면접 한 번이다. 돈을 받은 대리인이 그냥 앉으면 그만이기 때문이다. 속설처럼 도는 카메라 요령들, 곧 얼굴 앞에서 손을 흔들어 보라거나 방을 한 바퀴 비추라거나 카메라를 창밖으로 돌려 보라는 요구는 조잡하게 조작된 영상은 드러낼 수 있어도, 자리에 앉아 미리 연습한 사람에게는 아무 소용이 없다. 손 흔들기를 권하는 바로 그 경보조차 그것을 판정이 아니라 하나의 걸림돌로 제시한다.
나머지 목록도 비슷하다. 인터넷 주소로 읽어 낸 위치는 흔한 도구로 쉽게 꾸며 낼 수 있다. 잘 꾸민 경력 프로필이나 코드 공유 페이지는 증거가 아니라 주장일 뿐이고, 이 무리는 그런 것을 주문 제작하듯 만들어 둔다. 문제없이 나온 신원 조회 결과는 훔친 신원이 존재한다는 사실만 확인해 줄 뿐인데, 그것이야말로 이들이 노리는 바다.
이 수법에 부딪혀도 살아남는 것은 지원자와 무관하게 따로 모은 증거다. 지난 직장과 학교는 이력서에 적힌 번호가 아니라 당신이 직접 찾은 번호로 그 회사나 학교에 전화를 걸어 확인한다. 신원 서류는 스캔본에서 이름만 읽는 것이 아니라 그 서류가 진짜인지 확인한다. 법적 이름과 급여, 은행, 세금, 배송 정보를 나란히 놓고, 그것들이 하나의 일관된 이야기를 하는지 살핀다.
논의에서 큰 몫을 한 생각은 둘이다. 첫째는 연속성이다. 신원을 사람과 한 번이 아니라 여러 번 묶어 둔다. 면접에서, 노트북을 건넬 때, 계정을 열 때, 그리고 첫 몇 주에 걸쳐 거듭 확인하는 것이다. 그러면 합격 뒤에 사람이 바뀌어도 그것이 드러난다. 둘째는 봉쇄다. 장비는 확인된 주소로만 보내고, 새 직원에게는 그 일에 필요한 접근 권한만 주며, 문자 메시지가 아니라 실제 하드웨어에 묶인 로그인 방식을 요구하고, 허가받지 않은 원격 조종 소프트웨어를 감시하며, 가장 민감한 작업은 두 번째 승인자를 거치게 둔다. 그러면 걸러지지 못하고 들어온 사람도 혼자서는 많은 것에 손대지 못한다.
여기서 보안과 공정성이라는 두 편이 충돌하는 대신 만난다. 같은 수준의 접근 권한을 두고 겨루는 최종 후보라면 모두 같은 확인을 받아야 한다. 추가 검증은 기록으로 남은 사실을 따라야 한다. 서로 맞지 않는 서류, 무관해 보이는 지원자들 사이에서 되풀이해 쓰인 은행 계좌나 주소, 나중 회의에 다른 사람이 나타난 일이 그런 사실이다. 말투나 이름, 나라, 외국 학위가 이유가 되어서는 결코 안 된다.
규정 준수에 초점을 둔 모델은 이것이 양쪽으로 작동한다는 법적 논거를 폈다. 미국의 차별 금지법은 외국인이든 미국인이든 출신 국가에 따라 지원자를 다르게 대하지 못하도록 보호하므로, 외국인처럼 보이는 사람에게 슬며시 절차를 더 얹는 일 자체가 책임 소지가 된다. 그것은 보안으로도 허술하다고 모든 모델이 짚었다. 정교한 사례일수록 훔친 신원과 현지 조력자를 쓰는 평범한 미국인의 모습으로 나타나기 때문이다. 말투로 사람을 골라내는 방식은 엉뚱한 사람을 잡고 정작 그 작전은 놓친다.
가장 날카로운 이견은 어떤 자리를 가장 가볍게 다뤄도 되느냐를 두고 나왔다. 한 모델은 흔한 원격 엔지니어링 자리를 낮은 위험 등급에 두려 했다. 위협의 전체 그림에 초점을 둔 모델이 강하게 맞섰다. 코드나 고객 데이터, 배포에 접근하는 자리야말로 이들이 지원하는 바로 그 자리이므로, 그것을 쉬운 통로로 만드는 것은 약점을 정책에 새겨 넣는 일이라는 것이다. 이 모델은 또 가장 민감한 자리에서는 대면 입사 절차가 있으면 좋은 것이 아니라 기본이 되어야 한다고 주장했다.
모델들은 그 생각의 한계에는 뜻을 같이했다. 대면 절차는 사기의 비용을 높이지만 문제를 매듭짓지는 못한다. 그 선고 사건이 보여 주었듯, 기꺼이 신원을 빌려주는 사람은 직접 나타난 뒤 실제 일은 해외의 누군가에게 넘길 수 있기 때문이다. 대면은 쓸모 있는 걸림돌일 뿐, 결승선이 아니다.
논의가 다다르는 쓸모 있는 전환은, 지원자가 외국인처럼 보이는지 묻기를 멈추고 더 단순한 네 가지 물음을 시작하는 것이다. 지원자가 내세운 신원이 당신이 직접 모은 증거로 뒷받침되는가. 면접부터 실제 일까지 같은 사람이 자리에 있는가. 기기와 결제, 로그인 양상이 계속 하나의 이야기를 하는가. 그리고 이 모든 것이 끝내 실패하더라도, 이 계정이 낼 수 있는 피해는 얼마나 되는가. 원격 채용자는 카메라 앞의 강렬한 한순간이 아니라 시간을 두고 버티는 사슬로 확인되며, 여기에 사슬이 끊겨도 견딜 수 있을 만큼 좁은 접근 권한이 함께한다.
North Korean operatives keep getting hired into Western companies as remote IT staff, and the newest tactic is using stand-ins to sit the live video interview in place of the real applicant. Have several models work through how a company can actually verify who it is hiring for a remote role, and where the line should fall between real security and treating every foreign applicant as a suspect. Lay out the concrete checks that hold up and the ones that only look reassuring.
Identity Verification and Security Architect · gpt-5.6-terra
My core position: treat this as an identity-integrity and access-control problem, not a nationality-screening problem. The threat is real: the FBI’s July 2025 alert explicitly says that someone may attend the initial interview while a different person performs the work, and documents the use of U.S.-based facilitators, false identities, device hosting, and deceptive location signals. A March 2026 DOJ case described facilitators helping overseas workers pass video interviews, drug tests, and fingerprinting under borrowed identities. (fbi.gov)
But “looks foreign,” an accent, an unusual name, a foreign degree, or use of a VPN are not reliable indicators of wrongdoing—and using them as such is both unfair and strategically weak. A capable fraud operation wants employers to rely on stereotypes rather than evidence.
What actually holds up: a layered proof of person, place, and work
No one control proves identity. The durable design is a sequence of independently sourced checks, with a clear escalation path when facts conflict.
1. Establish the legal p…
HR Compliance and Global Operations Strategist · claude-sonnet-5
Good — this confirms exactly what I need to make my point sharp. Let me build on the Architect's technical framework by grounding the compliance and fairness side, because a security-only lens will get a company sued, and a compliance-only lens will get it infiltrated. Both failure modes are live right now.
The legal ground has shifted under everyone's feet
Two things changed since 2023 that make this debate more than theoretical:
First, remote I-9 verification is now a real compliance track — with teeth. DHS's alternative procedure lets E-Verify-enrolled employers examine documents "via live video instead of in person," but this isn't a rubber stamp. Pre-recorded video, email exchanges, asynchronous photo submissions, and chat-based tools do not satisfy the rule — the reviewer must see the person and the document together, in real time, with enough clarity to assess both. And enforcement has gotten sharper: failing to check the "alternative procedure" box is classified as a substantive violation under March 2026 ICE guidance, meaning it cannot be cured after a Notice of Inspection and is immediately finable. This matters for our topic directly — if the video moment itsel…
Threat Intelligence and Geopolitical Risk Analyst · grok-4-6
I’ll ground this in the latest official reporting on the DPRK remote-IT worker campaign and the stand-in interview tactic, then argue where verification actually holds and where it becomes profiling.The reporting already shows the scheme has moved past stolen IDs into live proxies and deepfakes; I’m pulling the July 2026 joint alert and a few primary FBI/DOJ records so the threat picture is sourced, not just recap.The other two seats have the architecture and the employment-law rails right. What they underweight is the threat model. This is not a clever freelancer scam that happens to involve foreigners. It is a state revenue-and-access program: thousands of skilled workers, operating in cells, using stolen or rented identities to get paid by Western firms and remit the proceeds to agencies that fund nuclear and ballistic-missile programs. The UN has put the haul in the hundreds of millions of dollars a year; a U.S.-led sanctions-monitoring assessment put 2024 earnings as high as $800 million.[[1]](https://www.nbcnews.com/tech/security/north-korea-worker-scheme-recruits-abroad-rcna596873)
That changes what “verify who you are hiring” has to mean.
The 2026 problem is no…
Researcher · gpt-5.6-terra
Research check — what the record supports, and what needs correction
Supported: the basic threat and the interview stand-in tactic
The central premise is well supported. In a July 23, 2025 alert, the FBI said U.S.-based facilitators have attended virtual interviews and meetings for DPRK IT workers. It expressly warned that *one person may pass the initial interview while another performs the job*. The FBI also documented laptop farms, U.S.-based device receipt, remote-access tooling, false identities, and payment-account facilitation.
Source: https://www.fbi.gov/investigate/cyber/alerts/2025/north-korean-it-worker-threats-to-u-s-businesses (fbi.gov)
A March 20, 2026 DOJ sentencing announcement independently corroborates this: three U.S. facilitators admitted enabling overseas IT workers to use their identities and pass employer vetting, including video interviews, drug tests, and fingerprinting; company laptops were then remotely accessed from overseas through unauthorized software.
Source: https://www.justice.gov/usao-sdga/pr/three-senten…
The Arbiter · gpt-5.6-sol
Round 1 record
The participants substantially agree on the governing principle: verify identity and maintain access security through evidence-based, role-specific controls—not nationality, accent, name, ethnicity, school, or intuition.
What the evidence establishes
The Researcher verified that:
- The FBI’s July 23, 2025 alert explicitly describes stand-ins attending interviews and warns that one person may interview while another performs the work.
- A March 20, 2026 DOJ case corroborates that facilitators helped overseas workers pass video interviews, drug tests, and fingerprinting under borrowed identities.
- The schemes involve laptop farms, false or stolen identities, unauthorized remote access, payment facilitation, data theft, extortion, sanctions evasion, and insider risk.
- FBI guidance supports direct verification of employment and education, controlled equipment shipping, payment and address reconciliation, comparison images across later meetings, live-video friction, and oversight of staffing vendors.
- EEOC guidance supports applying the same screening standards consistently rather than imposing extra checks on people who appear or sound foreign.…
Identity Verification and Security Architect · gpt-5.6-terra
Identity Verification and Security Architect — final position
The implementable answer is not “catch every DPRK operative in an interview.” It is: make it difficult to substitute a person, hard to reuse a false identity at scale, and low-impact if a deceptive hire gets through. A single video call—however polished—is not an identity system.
The FBI’s current public guidance is unusually direct: facilitators have attended virtual interviews and meetings on behalf of DPRK IT workers, and sometimes the interviewer and the person doing the job are different people. It recommends direct credential checks, repeated image comparison, controlled shipping, payment-pattern review, and particular scrutiny of contracted IT work. (fbi.gov)
A practical assurance matrix
| Role / access tier | Mandatory identity controls | Access controls | Escalate when… |
|---|---|---|---|
| Tier 1: ordinary remote work — no production, secrets, customer records, or admin access | Government-ID authentication through a vetted process; direct verification of material employment/education claims…
HR Compliance and Global Operations Strategist · claude-sonnet-5
This is genuinely useful ground truth, and it sharpens my position rather than softening it. Two things came back from my check worth flagging directly.
First, on I-9: my instinct that this is a live compliance trap was right, but the actual mechanism is different from what I implied last round, and I want to correct my own record. There's no March 2026 "instant fine" rule for the checkbox. What's real is this: DHS extended relaxed enforcement multiple times, with the latest extension giving employers until March 31, 2026 to physically re-inspect documents for any I-9s completed remotely or under relaxed rules between March 2020 and that deadline. That deadline has now passed as of this conversation. So the operative risk isn't a novel penalty category — it's that any company still carrying I-9s from that window without the physical re-check is now sitting on a compliance backlog that ICE can flag on inspection. That's a correction to my own claim, not a defense of it, and I'd rather say so than let it stand uncorrected.
Separately, the EEOC angle is more consequential than either of the technical participants have engaged with, and the search confirms it cuts a different dir…
Threat Intelligence and Geopolitical Risk Analyst · grok-4-6
I need current, primary-source material before I lock a final position—especially after the last round’s unverified alert. I’ll check FBI/DOJ/State guidance and recent case reporting, then map that onto the Architect’s matrix and HR’s fairness line.The July 2026 joint alert is real this time—I’ll pull the primary pages so the recommendations and the stand-in/deepfake language come from the governments themselves, not secondary write-ups.Threat Intelligence and Geopolitical Risk Analyst — final position
I am going to be blunt about what this is, because the hiring conversation keeps sliding toward “better interviews” when the adversary has already moved past interviews.
This is a state revenue-and-access program, not a résumé-quality problem. North Korean IT workers generate income for a WMD and ballistic-missile program, then use the same access to steal code, credentials, and crypto, and sometimes to extort the company that hired them. That is the FBI’s own framing, not mine.[[1]](https://www.fbi.gov/file-repository/cyber-alerts/north-korean-it-workers-conducting-data-extortion)
The July 31, 2026 joint alert is real and on the State Department site. Eleven governments —…
Researcher · gpt-5.6-terra
Final verification check
Confirmed: the FBI supports the central security model
The Architect and Threat Analyst are on solid ground that this is not solved by one video interview. The FBI’s July 23, 2025 alert says U.S.-based facilitators have attended virtual interviews and meetings for DPRK IT workers, and explicitly warns that the person who passes an initial interview may differ from the person who performs the work. The FBI recommends direct employment/education checks, comparison images for future meetings, controlled equipment delivery, payment-pattern review, and scrutiny of third-party staffing arrangements.
Source: https://www.fbi.gov/investigate/cyber/alerts/2025/north-korean-it-worker-threats-to-u-s-businesses (fbi.gov)
The FBI’s January 23, 2025 extortion alert also supports the access-control half of the proposed matrix: least privilege, no unnecessary local-admin rights, investigation of remote-access tooling and unusual multi-country logins, and monitoring for code/data exfiltration.
Source: https://www.fbi.gov/investigate/cyber/alerts/2025/north-ko…
The Arbiter · gpt-5.6-sol
Round 2 record
The debate converged on a practical model: identity assurance must be layered across hiring, onboarding, device use, payment, and access—not concentrated in a single interview. The purpose is not to prove an applicant’s loyalty or nationality, but to make substitution detectable and ensure that a deceptive hire cannot cause disproportionate harm.
Agreed assurance matrix
Tier 1 — low-impact remote roles
For roles without production, sensitive-data, administrative, financial, or secrets access:
- Authenticate identity through a vetted process.
- Verify material employment or education claims through independently obtained channels.
- Reconcile legal identity, payroll, and equipment-delivery details.
- Repeat the identity check before account activation.
- Issue a managed endpoint with phishing-resistant MFA, no local administration, and least privilege.
Tier 2 — technical, data, and contractor roles
Any role involving repositories, deployments, customer data, internal IT, or materially sensitive systems should receive Tier 1 controls plus:
- A second identity-binding event at equipment receipt or onboarding.
- Reconciliation among HR, payroll…
The Arbiter's Final Verdict · gpt-5.6-sol
Verdict
A company cannot reliably verify a remote hire through one “strong” interview or identity check. The defensible solution is a chain of identity continuity:
> Verify the legal identity independently, bind that identity to onboarding and equipment, confirm that the same person continues to appear and work, and limit what any new hire can do until trust is earned.
This should be applied according to role risk, not perceived nationality.
Checks that hold up
| Control | Why it matters |
|---|---|
| Authenticate identity documents through a vetted process | Better than accepting scans or screenshots, though not sufficient alone. |
| Verify employment and education through independently sourced contacts | Avoids applicant-controlled references and fabricated channels. |
| Reconcile identity, payroll, bank, tax, shipping, and contact details | Substitution schemes often develop inconsistencies across systems. |
| Repeat identity binding at interview, equipment receipt, activation, and early employment | Directly addresses the possibility that one person interviews and another works. |
| Ship managed equipment only to a verified address, with revi…